Wednesday, May 11, 2011

Symantec says Facebook apps leak personal data

Security company Symantec claims Facebook application coding error may allow third parties to access users' private details...

Facebook applications may leak users' private data to third parties, including advertisers, according to researchers at security giant Symantec.

The social network site allows third party applications, the most popular of which are games, to run inside an iFrame, a partition within a web page that allows it to run code from an external site.

Symantec claims that due to a coding error, Facebook's iFrame applications leak 'access tokens' to third parties such as advertisers or web analytics providers, granting them permission to access users' photos, messages and personal data.

"We estimate that as of April 2011, close to 100,000 applications were enabling this leakage," wrote Symantec research Nishant Doshi in a company blog post "We estimate that over the years, hundreds of thousands of applications may have inadvertently leaked millions of access tokens to third parties."

The company believes that those parties may not have realised that they could access that data.

Symantec has informed the social networking giant of the issue, it says. "Facebook notified us of changes on their end to prevent these tokens from getting leaked." It recommends that Facebook users change their passwords.

It is not the first time Facebook has been accused of inadvertantly leaking users' private data. In October last year, two Facebook users sued the company, alleging that the 'referrer headers' that tell advertisers when a user has clicked on an ad contain private data about that user's browsing history.

Facebook denied the charges, arguing that there had been no material damage as a result of the practice. A similar suit has since been launched against LinkedIn, the professional social network popular in the IT industry.

Read more at :http://www.information-age.com/channels/security-and-continuity/news/1623178/facebook-apps-leak-personal-data-says-symantec.thtml

Google Chrome OS laptop rentals for $20 a month


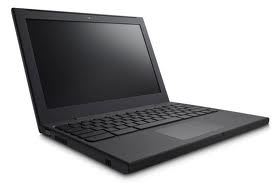
Google is set to unveil a Chrome laptop “student package” tomorrow at its I/O developer conference for $20 a month, an unnamed senior Google executive tells Forbes.

If true, the move has the potential to completely reshape the way consumers adopt computers, and it will also serve as a not-so-subtle Trojan horse for Google’s online offerings.

The $20 monthly fee will cover both hardware and online services for the laptops, which run Google’s web-centric Chrome OS software, the executive said. It will likely serve as a precursor to an enterprise Chrome laptop offering, wherein businesses pay a slight premium over their $50 annual fee for Google Apps (the company’s web-based Microsoft Office competitor suite).

The Chrome laptops will likely feature the same mobile broadband capabilities as the CR-48. That computer shipped with built-in 3G access and included 100 megabytes of monthly internet free for two years. You could also opt for daily unlimited internet for $10, 1 gigabyte of mobile internet for $20 a month, 3 GB for $35 a month, and 5 GB for $50 a month.

Aiming the Chrome laptop subscriptions at students seems like a good choice at first glance. After all, paying $20 a month for a computer beats spending $600 or more for a full-fledged laptop. But most students would have a hard time relying solely on the Chrome laptops, since they won’t have access to key Windows and Mac software that some courses may require. Like netbooks, the Chrome laptops could serve as secondary machines — assuming they’re light enough.

Google will also need to offer students something far better than its CR-48 laptop, which was heavy and had one of the worst trackpads ever forced upon a computer.

Reports of a Chrome laptop subscription plan go back a few weeks, when Neowin heard pretty much the same information Forbes did today from a “reliable source.” That report also noted that Google will upgrade the Chrome laptop hardware and offer hardware replacements for the life of the subscription

Read more at http://venturebeat.com/2011/05/10/chrome-os-laptop-rentals/

Friday, February 18, 2011

Microsoft affirms Windows Zero Day Vulnerability


Microsoft confirmed Wednesday that a previously unknown heap buffer overflow vulnerability can affect the browser service module in Windows.

The vulnerability was first disclosed on Monday, in a Valentine's Day gift to Microsoft, when a security researcher released details and proof-of-concept exploit code.

The server message block (SMB) vulnerability exists "inside an error-reporting function of the CIFS (common Internet file system) browser service module," said Matt Oh, a security researcher at Microsoft, in a blog post.

Recent research reveals the common characteristics of virtualization success, what barriers companies face, and how to get the most from your virtualization efforts.

"The State of Enterprise Efficiency in the Virtual Era"

Microsoft didn't receive any advance notification of the vulnerability. "Luckily, the [proof of concept] was not fully weaponized -- that is, it was not designed to achieve remote code execution, just a denial of service -- although it has been reported as being a remote code execution vulnerability," said Oh.

Security vulnerability information service Vupen rates the bug as "critical," noting that it could be used to not just create a denial of service, but also to remotely run exploit code on a computer.

But despite Vupen's assessment, the bug may not be remotely exploitable. For starters, the security researcher who disclosed the flaw, Cupidon-3005 (French for cupid), rated the risk of remote exploitability as unlikely. Likewise, security researchers at Microsoft said they haven't been able to exploit the bug remotely. That's because the attack works by joining multiple strings of data, yet an attacker can't control where the data ends up, which makes injecting exploit code -- at least theoretically -- not possible.

"Our conclusion is that the part of the string that the attacker can control will always end up inside the allocated buffer, and the part the attacker can't control is in the part that overflows the buffer," said Oh. "As a result, we don't (yet) see how [remote code execution] can happen."

While the exploit likely only affects local network segments, "all versions of Windows are vulnerable, although the issue is more likely to affect server systems running as the Primary Domain Controller (PDC)," said Mark Wodrich, a security software engineer at Microsoft, in a blog post. "In environments following best practices, the browser protocol should be blocked at the edge firewalls, thus limiting attacks to the local network."

Blocking the browser protocol requires blocking or filtering UDP and TCP ports 138, 139, and 445.


Thursday, February 17, 2011

Google's ‘One Pass’ subscription solution for publishers


Just one day after Apple made its App Store subscription service available to publishers, Google has already responded by announcing a similar service for its Android platform. The solution will also work in Web-based clients, allowing publishers to reach users on multiple platforms with a single solution. Much like Apple’s implementation, Google’s One Pass provides users with a single interface where they can access and manage all of their digital newspaper, magazine and other content subscriptions. Unlike App Store subscriptions, however, Google gives publishers much more freedom with regard to pricing models and flexibility. Publishers will also be able to give free or reduced subscriptions to paid print subscribers, and they can even utilize a freemium model if they so desire. Hit the break for a video from Google outlining the One Pass product.